Table of Contents
PII (Personally Identifiable Information) is any data that can identify you directly or indirectly, such as your name, email, phone number, IP address, or location. When exposed, PII enables identity theft, fraud, phishing and account takeover.
Once you understand what qualifies as Personally Identifiable Information (PII), the next challenge is recognizing where it exists, how it’s used and why it is so heavily targeted.
In modern digital systems, PII is not limited to obvious identifiers like names or ID numbers. It is embedded in logs, analytics tools, cloud platforms, mobile apps and everyday business processes.
This matters because PII is often the starting point for cyberattacks. When exposed, it enables identity theft, account takeover, personalized phishing and long-term privacy violations.
Many organizations underestimate their PII exposure, not because they collect sensitive data intentionally, but because indirect or technical data can still identify individuals when combined.
In the sections below, you’ll see real-world examples of PII, understand how attackers exploit it and learn practical ways to protect it across security, compliance and operational environments.
Check out our latest blog on : Google Gmail Data Breach: What’s Actually Happening (2026)
What Is PII?

Personally Identifiable Information (PII) is any data that can be used to identify a specific individual, either on its own or when combined with other available information.
The identification does not need to be immediate or obvious; if there is a reasonable way to link the data to a real person, it qualifies as PII.
PII is not limited to obvious identifiers like names or passport numbers. In modern digital systems, even technical and behavioral data such as IP addresses, device identifiers, or location history can function as PII when they point back to a unique individual.
At its core, PII answers one question:
“Can this information identify a real person, directly or indirectly?”
If the answer is yes, the data should be treated as PII.
Read More On Nintendo Direct 2026: Security Risks & What to Watch
Direct vs Indirect Identification
PII is broadly classified based on how it identifies a person.
Directly Identifiable PII
This data can identify a person without needing any additional information:
Full name
Email address
Mobile number
Government-issued ID numbers
Passport or driver’s license
Biometric identifiers
If leaked, this data immediately exposes an individual.
Indirectly Identifiable PII
This data may not identify someone by itself, but it becomes PII when combined with other data:
IP address
Date of birth
Gender
ZIP or postal code
Device ID
Browser fingerprint
Job title and employer
For example, a ZIP code alone is not enough, but a ZIP code + date of birth + gender can uniquely identify a large percentage of individuals.
Check out our latest blog on Data Leak Prevention: Complete Guide, Tools & Best Practices
PII Exists Across Formats and Systems
PII is not restricted to databases or forms. It exists in multiple formats:
Structured data
Stored in databases, CRMs, HR systems, spreadsheetsUnstructured data
Emails, PDFs, chat logs, call recordings, support ticketsDigital identifiers
Cookies, session IDs, tracking pixelsPhysical records
Printed forms, ID copies, contracts
Many data breaches occur because organizations protect databases well but ignore unstructured PII, such as emails or cloud file shares.
Check out our latest blog on What Is The Goal Of An Insider Threat Program?
PII Is Context-Dependent
Whether data qualifies as PII often depends on context.
Examples:
A first name alone may not be PII
A first name + company + job title may become PII.
An IP address in isolation may seem technical.
The same IP address tied to a user account becomes PII.
This is why privacy laws and cybersecurity frameworks emphasize data context, not just data fields.
PII in the Digital Era
With cloud computing, analytics and AI systems, the definition of PII has expanded significantly.
Modern PII includes:
Online identifiers
Behavioral data
Location tracking
Voice recordings
Facial recognition data
Chatbot conversations
Session replays and heatmaps
Many organizations unknowingly collect PII through third-party tools such as analytics platforms, ad trackers, chat widgets and CRM integrations.
Read More On: Data Risk Management Framework: Strategy (2026)
Why Correctly Identifying PII Matters
Misclassifying data as “non-sensitive” when it is actually PII can lead to:
Regulatory violations
Data breaches
Legal penalties
Loss of customer trust
From a cybersecurity and compliance perspective, you cannot protect what you don’t correctly identify.
That is why PII identification is always the first step in:
Data protection programs
Privacy impact assessments
Risk assessments
Compliance audits
Incident response planning
Common Examples of PII

Personally Identifiable Information appears across everyday systems, business workflows and digital platforms often in places people don’t immediately consider “sensitive.”
Below are context-based, real-world examples of PII, grouped by how and where the data is actually collected and used.
PII in Business and Workplace Systems
Organizations routinely collect PII as part of normal operations, especially in HR, finance and internal IT systems.
Common workplace PII includes:
Employee records containing personal contact details
Bank account numbers used for salary disbursement
Tax identification numbers
Emergency contact details
Performance reviews tied to individual employees
Access logs showing who logged in and when
Even internal tools such as attendance systems, VPN logs, badge access records and device inventories often store PII because they link activity to specific individuals.
Check out our latest blog on Digital Risk Protection for Enterprise Security
PII in Websites, Forms and Online Services
Websites and SaaS platforms collect PII far beyond simple contact forms.
Examples include:
Newsletter subscriptions linked to user profiles
Account registration details
Password reset requests
Comment sections tied to user accounts
Chatbot conversations containing personal queries
Support tickets and complaint submissions
Booking and appointment systems
What makes this data especially sensitive is that it is often exposed to:
Third-party plugins
Analytics tools
CRM integrations
Email marketing platforms
A single misconfigured plugin can expose thousands of user records.
PII in E-Commerce and Payment Systems
Online transactions involve multiple layers of personal data across different systems.
Common examples include:
Billing and shipping addresses
Order history tied to customer profiles.
Payment confirmation emails
Refund and dispute records
Saved customer preferences and wish lists
Purchase behavior linked to accounts
Even if payment data is processed by third-party gateways, customer identity and transaction metadata still count as PII and remain the business’s responsibility.
PII in Mobile Apps and Devices
Mobile platforms collect highly granular personal data, often automatically.
Examples include:
Device identifiers and app instance IDs
Location data (real-time or historical)
Call logs and contact access (with permission)
Push notification tokens linked to users.
App usage patterns tied to individual accounts
Because mobile data is continuous and persistent, it poses a higher privacy risk if breached or misused.
PII in Marketing and Analytics Tools
Modern marketing heavily relies on user-level data tracking.
Examples include:
Email campaign lists with engagement history
CRM records showing lead source and behavior
Retargeting audience data
Conversion tracking is linked to a user session.s
Cookies associated with known users
Heatmaps and session recordings
When marketing data is combined with identity information, it clearly qualifies as PII even if collected for “analytics” purposes.
PII in Communication Channels
Every day, communication systems store large volumes of unstructured PII.
Common sources include:
Emails and attachments
Recorded customer support calls
Live chat transcripts
Video conferencing recordings
Internal messaging platforms
These systems are often overlooked in security planning, yet they are frequent sources of data leaks.
PII in Cloud Storage and File Sharing
Cloud platforms are a major source of accidental PII exposure.
Examples include:
Shared spreadsheets with customer data
Publicly accessible folders
Backup files stored without encryption
Exported CRM or database files
Old reports containing personal data
Many real-world breaches occur not from hacking, but from misconfigured cloud permissions.
PII in Logs and Security Data
From a cybersecurity perspective, even security tools themselves collect PII.
Examples include:
Authentication logs
SIEM event data tied to users
Audit trails
Endpoint activity logs
While essential for security monitoring, these logs must still follow privacy and data retention rules.
Why These Examples Matter
PII is not limited to obvious identity fields. It exists:
Across departments
Across tools and vendors
Across structured and unstructured data
Across production, backup and log systems
Most organizations already collect far more PII than they realize. The challenge is not collection but visibility, classification and protection.
Types of PII: Sensitive vs Non-Sensitive
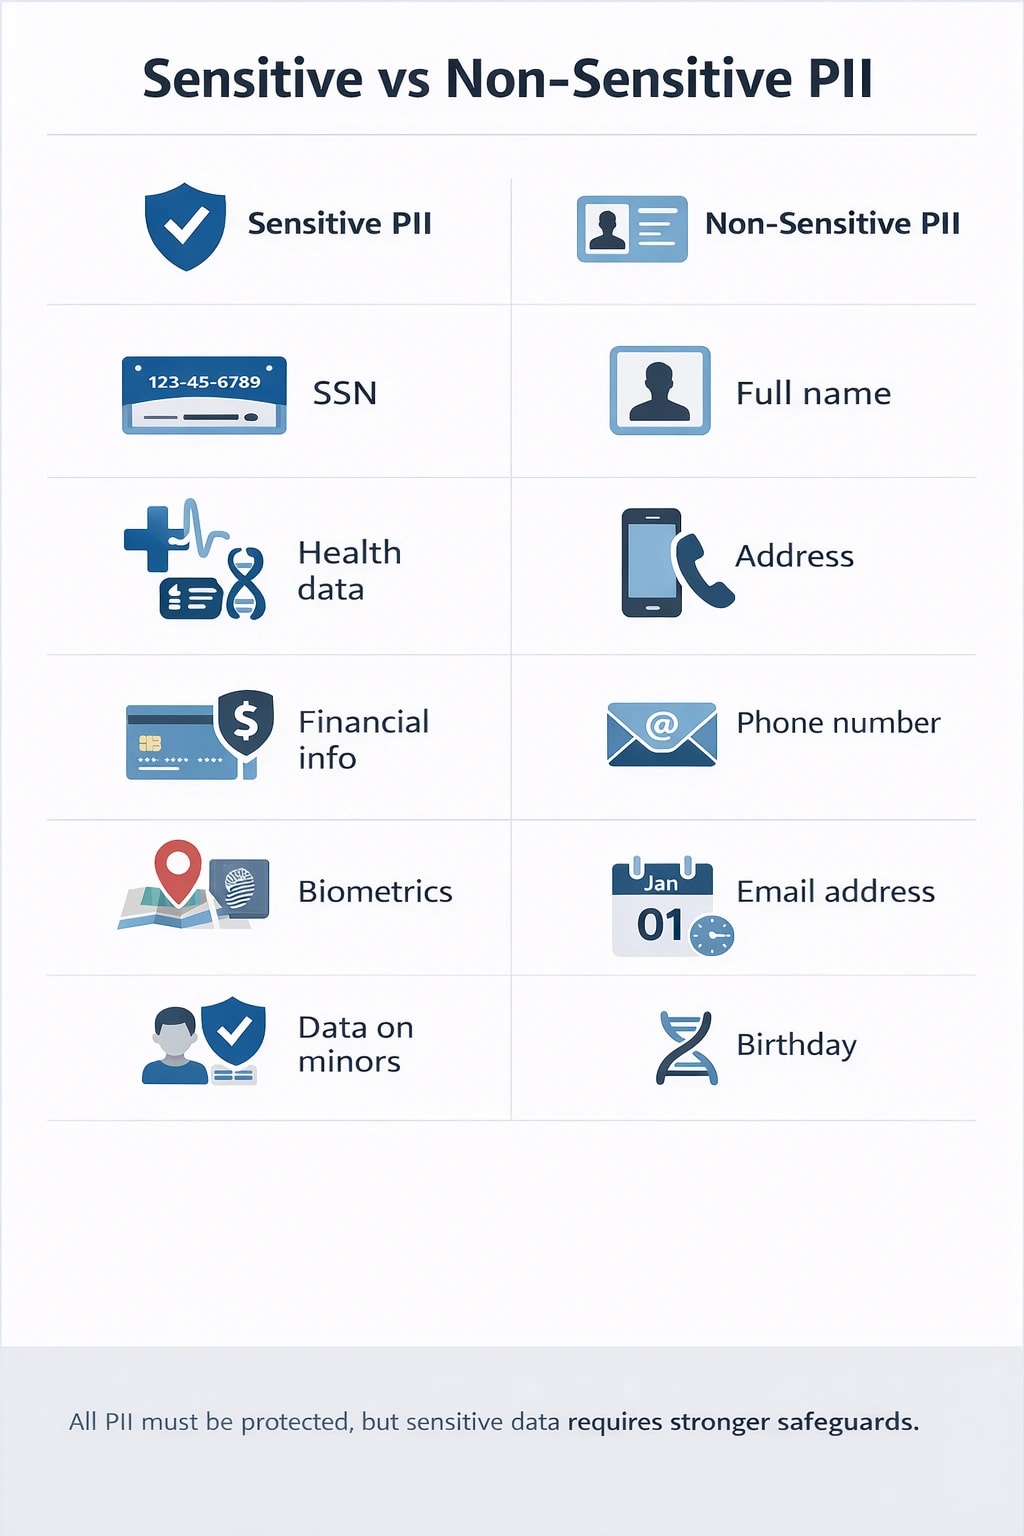
Not all Personally Identifiable Information carries the same level of risk. Some data can cause minor inconvenience if exposed, while other data can lead to financial loss, identity theft, or long-term personal harm.
This difference is why PII is categorized into non-sensitive and sensitive types.
Understanding this distinction is critical for deciding how data should be stored, accessed, encrypted, shared and retained.
Non-Sensitive PII
Non-sensitive PII includes personal information that is generally low risk when exposed on its own, especially if it is publicly available or commonly shared in professional or social contexts.
This type of PII typically:
Does not directly enable fraud
Cannot be misused without additional data
It is often visible in public or semi-public settings.
Still requires protection, but with lower control intensity.
From an operational perspective, non-sensitive PII is often used in:
User profiles
Customer communication
Basic personalization
Marketing segmentation
Public directories
However, the key risk with non-sensitive PII is aggregation. When multiple low-risk data points are combined, they can quickly cross the line into sensitive territory.
This is why many breaches involving “harmless” data still lead to serious consequences.
Sensitive PII
Sensitive PII includes information that can cause direct and immediate harm if exposed, misused, or stolen. This data typically enables impersonation, financial fraud, account takeover, or permanent identity compromise.
Sensitive PII usually:
Requires strict access control
Must be encrypted by default
It is regulated more heavily by law.
Triggers mandatory breach notifications
Has a long-term impact if leaked
In practice, sensitive PII is treated as high-value data, similar to credentials or cryptographic keys. Security teams often isolate it into restricted systems, apply stronger monitoring and limit employee access.
Risk Comparison: Sensitive vs Non-Sensitive PII
Factor | Non-Sensitive PII | Sensitive PII |
Abuse potential | Low alone | High |
Breach impact | Limited | Severe |
Legal exposure | Moderate | High |
Storage controls | Standard security | Strong encryption & isolation |
Access scope | Broader | Strictly limited |
Retention period | Flexible | Minimized |
This risk-based approach is how regulators and auditors expect organizations to classify data.
Why Classification Matters in Practice
Correctly classifying PII determines:
What encryption standards apply
Who can access the data?
Whether MFA is required
How long can data be retained?
How incidents are reported
Which vendors are allowed to process the data
Many compliance failures occur not because data was stolen, but because it was misclassified and under-protected.
Regulatory View on Sensitive vs Non-Sensitive PII
Most privacy laws adopt a tiered protection model, even if they use different terminology.
Common regulatory expectations:
Sensitive PII requires explicit user consent
Additional safeguards must be applied.
Data minimization is mandatory.
Purpose limitation is enforced.
Breach reporting timelines are shorter.
In audits, regulators rarely ask whether you collect data; they ask how you classify and protect it.
Operational Challenges Organizations Face
Real-world challenges include:
Over-collecting sensitive PII “just in case.”
Storing sensitive and non-sensitive data together
Sharing sensitive PII with third-party vendors
Retaining data longer than required
Lack of visibility into unstructured data
Without proper classification, even strong security tools fail to reduce actual risk.
Key Takeaway
The difference between sensitive and non-sensitive PII is not academic; it directly affects security design, compliance posture and breach impact. Organizations that treat all PII the same either overspend on controls or expose themselves to serious legal and security risks.
Effective data protection starts by applying the right level of protection to the right type of PII.
PII vs Personal Data vs PHI

The terms PII, Personal Data and PHI are often used interchangeably, but they are not the same.
Each term comes from a different legal and regulatory context and carries distinct compliance, security and handling requirements.
Understanding the differences is especially important for organizations operating across regions or industries.
PII (Personally Identifiable Information)
PII is a term most commonly used in cybersecurity, risk management and U.S.-centric regulations. It focuses on whether data can be used to identify or trace an individual’s identity.
From a security standpoint, PII is treated as:
Data that must be protected from unauthorized access
A primary target in data breaches
A key component in identity theft and fraud
PII is frequently referenced in:
Security policies
Incident response plans
SIEM and logging strategies
Risk assessments
The PII concept is heavily used by security teams because it aligns well with threat modeling and breach impact analysis.
Personal Data
Personal Data is the term used by the GDPR and most modern privacy laws outside the United States. It has a broader scope than PII and includes data that may not traditionally be considered identifying in a security context.
Personal data covers:
Online identifiers
Digital behavior
Location and device data
Technical identifiers used by platforms and apps
What makes personal data distinct is its privacy-first approach. The focus is not just on identification, but on:
How data is collected
Why is it processed
Whether consent exists
How long is it retained?
Under privacy laws, even data that poses a low security risk may still trigger legal obligations.
PHI (Protected Health Information)
PHI is a specialized category of personal data defined under healthcare regulations, most notably HIPAA in the United States. It applies only when personal data is linked to health, medical, or healthcare services.
PHI is subject to:
Strict access controls
Mandatory audit logging
Detailed breach notification rules
Industry-specific compliance audits
PHI includes medical, billing and insurance-related information when it is associated with an identifiable individual. Because of its sensitivity, PHI often receives the highest level of protection within organizations.
Key Differences at a Glance
Aspect | PII | Personal Data | PHI |
Primary focus | Identification | Privacy & rights | Healthcare data |
Used mainly in | Security & risk | Privacy laws | Healthcare regulations |
Scope | Moderate | Broad | Narrow but strict |
Industry-specific | No | No | Yes |
Highest compliance burden | Medium | High | Very high |
How These Terms Overlap
The relationship between these terms is hierarchical:
PHI is always personal data
PHI is always PII
Personal data may not always be PII in a security sense.
PII may not always qualify as PHI
This overlap often confuses audits and compliance reviews, especially for organizations that operate in both healthcare and non-healthcare sectors.
Why the Distinction Matters for Organizations
Using the wrong classification can lead to:
Incomplete compliance programs
Incorrect breach notifications
Over- or under-protection of data
Regulatory penalties
Audit failures
For example, treating GDPR personal data only as PII may cause an organization to ignore consent, transparency and data subject rights, even though those are mandatory under privacy laws.
Practical Rule to Follow
Security teams should focus on PII and PHI.
Privacy and legal teams should focus on personal data and PHI.
Healthcare organizations must treat PHI as the highest-risk category.
When in doubt, organizations should apply the strictest applicable standard.
Why PII Is So Important
Personally Identifiable Information sits at the intersection of privacy, security, compliance and trust. Its importance goes far beyond technical data handling it directly affects individuals, businesses, regulators and digital ecosystems.
Understanding why PII matters is essential for making informed decisions about how data is collected, processed, stored, shared and retained.
PII Represents Real People, Not Just Data
At its core, PII is tied to human identity. When PII is mishandled, the impact is personal financial stress, identity theft, reputational harm and loss of privacy.
Unlike other types of business data:
PII cannot be changed easily
Once exposed, the damage may be permanent.
Individuals bear the consequences long after the incident.
This human impact is why privacy laws and ethical data practices place such strong emphasis on protecting PII.
PII Is Central to Trust and Brand Reputation
Customers, users and employees trust organizations with their personal data. That trust is fragile.
Poor PII handling can result in:
Loss of customer confidence
Increased churn
Negative media coverage
Reduced user engagement
Long-term brand damage
In many industries, trust is a competitive advantage. Organizations that demonstrate strong PII protection often see higher customer loyalty and better market perception.
PII Drives Legal and Regulatory Accountability
PII is the primary focus of modern data protection laws worldwide. Regulators care less about what technology you use and more about how you protect personal data.
Why this matters:
Fines can reach millions
Audits are becoming more frequent.
Breach notification timelines are strict.
Non-compliance affects cross-border operations.
In most investigations, the question is not whether a breach occurred but whether reasonable safeguards were in place to protect PII.
PII Is a High-Value Target for Cybercriminals
From an attacker’s perspective, PII is valuable because it:
Enables fraud and impersonation
Can be reused across platforms
Has resale value on illicit markets
Supports social engineering attacks
Even partial PII datasets can be weaponized when combined with other leaked information. This makes PII a priority asset for threat actors and a priority defense concern for organizations.
PII Influences Security Architecture and Risk Management
PII classification directly affects:
Security control design
Encryption requirements
Access management models
Monitoring and logging strategies
Incident response planning
Without identifying where PII resides, organizations cannot:
Accurately assess risk
Prioritize security investments
Design effective controls
Respond quickly to the incident.s
PII awareness is the foundation of any mature cybersecurity program.
PII Affects Business Operations and Scalability
As organizations grow, the volume of PII they handle increases across:
Customer databases
Employee systems
Marketing platforms
Cloud services
Third-party vendors
Failure to manage PII properly can slow expansion, complicate partnerships and block entry into regulated markets. Strong PII governance, on the other hand, enables:
Faster compliance approvals
Easier vendor onboarding
Safer data sharing
Global scalability
PII Is Essential for Ethical Data Use
Beyond legal requirements, PII raises ethical questions:
Should this data be collected?
Is it truly necessary?
Is the user aware?
Is consent meaningful?
Organizations that treat PII responsibly demonstrate respect for user autonomy and privacy an increasingly important in digital ethics and corporate responsibility.
PII Protection Is No Longer Optional
In today’s environment:
Users expect transparency
Regulators expect accountability
Partners expect compliance
Attackers expect weaknesses
Ignoring PII protection is no longer a technical oversight; it is a strategic failure.
PII in Cybersecurity and Data Breaches

In cybersecurity, PII is treated as a high-impact asset because its exposure directly translates into real-world harm.
Most security incidents are not measured by systems affected, but by how much PII was exposed and how sensitive that data was.
For security teams, PII defines breach severity, response urgency, legal obligations and recovery cost.
Why PII Is the Primary Metric in Breaches
When a breach occurs, investigators immediately ask:
What PII was accessed?
How many individuals are affected?
Was sensitive PII involved?
Was the data encrypted?
Can individuals be identified?
The presence of PII determines:
Whether the incident is legally reportable
How quickly must regulators be notified?
Whether affected individuals must be informed
The level of regulatory scrutiny that follows
A system outage may be inconvenient. A PII breach is legally and reputationally damaging.
Common Attack Paths That Lead to PII Exposure
Most PII breaches do not involve advanced exploits. They result from basic security failures along predictable paths:
Compromised credentials granting database or CRM access
Misconfigured cloud storage or backup systems
Insecure APIs exposing user records
Phishing attacks targeting employees with access to PII
Excessive user privileges and weak access segmentation
Lack of monitoring on data access patterns
In many incidents, attackers simply log in and download data rather than exploit vulnerabilities.
Why PII Breaches Are Hard to Detect
PII exposure often occurs silently.
Reasons include:
Legitimate user accounts are abused
Data access looks “normal” in logs.
Large exports are not monitored.
Unstructured data is rarely inspected.
Security tools focus on malware, not data misuse.
As a result, many organizations discover PII breaches weeks or months after they occur, increasing regulatory and reputational damage.
Role of PII in Incident Response
Once a breach is suspected, PII becomes the central focus of incident response.
Security teams must:
Identify which systems contained PII
Determine what data was accessed or exfiltrated.
Assess whether the data was encrypted or tokenized.
Classify the sensitivity level of exposed PII.
Coordinate with legal and compliance teams.
Incident response timelines are driven not by technical recovery, but by PII exposure assessment.
PII and Breach Notification Obligations
Most data protection laws tie breach notification requirements directly to PII exposure.
Key factors regulators examine:
Type of PII involved
Volume of affected individuals
Likelihood of harm
Security controls are in place
Speed of detection and response
Organizations that cannot clearly demonstrate PII awareness and control often face harsher penalties even if the breach itself was limited.
PII as a Long-Term Risk After Breaches
Unlike passwords or tokens, many forms of PII cannot be reset.
Long-term risks include:
Persistent identity fraud
Reuse of data in future attacks
Increased phishing effectiveness
Blackmail or social engineering
Ongoing legal liability
This long-tail risk is why regulators treat PII breaches more seriously than other security incidents.
Security Controls Designed Specifically for PII
Modern cybersecurity strategies increasingly focus on data-centric security.
Controls designed to protect PII include:
Data classification and tagging
Encryption at rest and in transit
Tokenization and data masking
Privileged access management
User behavior analytics
Data loss prevention (DLP)
Continuous audit logging
Without identifying where PII resides, these controls cannot be applied effectively.
Why Most Organizations Struggle With PII Security
Common challenges include:
Lack of visibility into unstructured data
Shadow IT and SaaS sprawl
Over-permissioned users
Weak vendor access controls
Inconsistent retention policies
Security failures often occur not because tools are missing but because PII is not clearly mapped and governed.
Laws and Regulations Governing PII
Personally Identifiable Information is regulated worldwide through privacy and data protection laws designed to limit misuse, enforce accountability and protect individual rights.
While terminology and scope vary by region, the underlying principle is consistent: organizations are responsible for safeguarding personal data throughout its lifecycle.
Understanding these laws is critical for compliance, risk reduction and cross-border operations.
Global Approach to PII Regulation
Most PII regulations are built around a few shared concepts:
Lawful and transparent data collection
Purpose limitation (data collected for a specific reason)
Data minimization
Security safeguards
Accountability and documentation
Rights for individuals
Where laws differ is in definitions, enforcement mechanisms, penalties and jurisdictional reach.
GDPR (General Data Protection Regulation – EU)
GDPR is one of the most comprehensive and influential privacy laws globally. It applies to any organization that processes personal data of individuals located in the European Union, regardless of where the organization itself is based.
Key characteristics:
Broad definition of personal data
Strong emphasis on consent and transparency
Mandatory data protection measures
Strict breach notification timelines
Significant financial penalties
GDPR shifted privacy from a regional concern to a global compliance standard, influencing laws in many other countries.
CCPA / CPRA (California, USA)
California’s privacy laws focus on consumer rights and transparency, particularly for businesses collecting personal data for commercial purposes.
Core aspects include:
Right to know what personal data is collected
Right to delete personal data
Right to opt out of data selling or sharing.
Disclosure obligations for businesses
Unlike GDPR, these laws are more consumer-centric and less prescriptive about technical security controls, but enforcement actions can still be substantial.
HIPAA (United States – Healthcare)
HIPAA governs how healthcare organizations handle health-related personal data. It applies specifically to covered entities and their business associates.
What makes HIPAA distinct:
Industry-specific scope
Detailed administrative, physical and technical safeguards
Mandatory audit controls
Breach notification rules tailored to healthcare
Organizations handling medical data must treat PHI as a special class of highly regulated PII.
UAE PDPL (United Arab Emirates)
The UAE Personal Data Protection Law establishes a national framework for personal data protection across most sectors.
Key highlights:
Consent-based processing model
Strong data subject rights
Data localization and cross-border transfer controls
Security and breach notification obligations
For organizations operating in or targeting the UAE, PDPL compliance is becoming increasingly important, especially for digital platforms and SaaS businesses.
India DPDP Act (Digital Personal Data Protection Act)
India’s DPDP Act introduces a modern privacy framework focused on digital personal data.
Core principles include:
Consent-driven data processing
Purpose limitation
Data fiduciary accountability
Breach reporting requirements
Penalties for non-compliance
The law reflects India’s growing focus on data sovereignty and digital trust.
Other Regional and Sectoral Laws
Many countries and industries enforce their own PII-related regulations, such as:
LGPD (Brazil)
POPIA (South Africa)
PIPEDA (Canada)
APPI (Japan)
Financial and telecom-specific regulations
For multinational organizations, compliance often means aligning with multiple overlapping frameworks.
Common Compliance Obligations Across Laws
Despite differences, most PII regulations require organizations to:
Clearly define why data is collected
Limit data to what is necessary.
Implement reasonable security controls.
Maintain records of processing activities.
Respond to data subject requests.s
Notify authorities and individuals after certain breaches.
Failing in any of these areas can trigger enforcement action.
Penalties and Enforcement Trends
Regulators are increasingly focused on:
Repeated violations
Lack of internal controls
Poor breach response
Inadequate documentation
Penalties may include:
Monetary fines
Business restrictions
Mandatory audits
Public enforcement notices
In many cases, reputational damage exceeds the financial penalty.
Why Understanding PII Laws Matters
PII laws affect:
Website design
Marketing practices
Data storage decisions
Vendor selection
Cloud architecture
Incident response planning
Organizations that treat compliance as an afterthought often struggle to scale or operate across borders.
How Organizations Should Protect PII

Protecting Personally Identifiable Information requires more than installing security tools. Effective PII protection is built on processes, controls, accountability and continuous oversight across the entire data lifecycle.
Organizations that succeed treat PII protection as a business-wide responsibility, not just an IT task.
1. Identify and Map PII Across the Organization
PII protection starts with visibility.
Organizations must know:
What PI do they collect
Where it is stored
How it flows between systems
Who can access it
Which third parties process it
This involves data mapping across:
Databases and CRMs
Cloud storage
Email systems
Logs and backups
Third-party platforms
Without accurate data mapping, security controls are applied blindly.
2. Apply Data Minimization and Purpose Limitation
Collecting less PII reduces risk.
Best practices include:
Collect only data required for a specific purpose
Avoid “just in case” data collection.
Remove unused fields from forms.
Periodically review the data necessity.
Data that does not exist cannot be breached.
3. Implement Strong Access Controls
Access to PII should be strictly limited.
Key measures:
Role-based access control (RBAC)
Least-privilege permissions
Multi-factor authentication for sensitive systems
Regular access reviews
Immediate access removal upon role change
Many breaches occur because users have more access than they need.
4. Encrypt PII at Rest and in Transit
Encryption is a fundamental protection mechanism.
Organizations should:
Encrypt databases containing PII
Use TLS for all data transfers.
Protect encryption keys securely.y
Avoid storing PII in plaintext.
Encryption reduces breach impact and is often considered a mitigating factor by regulators.
5. Use Data Masking, Tokenization and Pseudonymization
These techniques reduce exposure without breaking functionality.
Examples:
Masking PII in non-production environments
Tokenizing sensitive fields in databases
Pseudonymizing data used for analytics
This limits how much real PII is exposed during daily operations.
6. Secure Unstructured and Shadow Data
Unstructured data is one of the biggest PII risks.
Protection strategies include:
Scanning file shares and cloud storage
Securing email systems
Controlling document sharing permissions
Applying retention policies
Most organizations underestimate how much PII exists outside core systems.
7. Monitor and Log Access to PII
Visibility into data access is essential.
Organizations should:
Log access to PII repositories
Monitor unusual data access patterns.
Detect large exports or abnormal queries
Integrate logs with SIEM platforms
Monitoring helps detect insider threats and compromised accounts early.
8. Secure Third-Party and Vendor Access
Vendors are a common source of PII exposure.
Best practices include:
Conducting vendor risk assessments
Limiting vendor access to required data only
Including data protection clauses in contracts
Monitoring vendor activity
Reviewing vendor compliance regularly
Your security posture is only as strong as your weakest vendor.
9. Establish Retention and Deletion Policies
Keeping PII indefinitely increases risk.
Organizations should:
Define clear retention periods
Automate deletion where possible
Securely dispose of physical and digital records
Remove outdated backups
Retention policies should align with legal and business requirements.
10. Prepare for Incidents Involving PII
PII-focused incident readiness is essential.
Organizations need:
Incident response plans that address PII
Defined roles for legal, security and communications teams
Breach assessment workflows
Clear notification procedures
Prepared organizations respond faster and reduce damage.
11. Train Employees on PII Handling
Human error is a major risk factor.
Effective training covers:
Identifying PII
Safe data handling practices
Phishing and social engineering awareness
Reporting suspected incidents
Employees are the first line of defense.
12. Review and Improve Continuously
PII protection is not static.
Ongoing efforts include:
Regular audits
Policy updates
Tool evaluations
Risk reassessments
As systems, regulations and threats evolve, PII protection must evolve too.
PII in Marketing, Websites and SaaS Platforms
PII is heavily used in digital marketing and SaaS environments.
Common PII collected online
Contact forms
Newsletter signups
CRM records
Analytics tools
Chatbots
Payment gateways
Best practices for websites
Collect only necessary data.
Display privacy policies clearly.
Use HTTPS everywhere
Limit third-party scripts
Secure databases and backups
Even basic websites can face legal risk if PII is mishandled.
Examples of PII Misuse (Real-World)
PII misuse does not always involve sophisticated cyberattacks. In many cases, it results from poor decisions, weak controls, or convenience-driven shortcuts.
These real-world patterns show how organizations commonly mishandle personal data often without malicious intent.
1. Collecting Excessive PII Without Business Need
One of the most common forms of PII misuse is over-collection.
Examples:
Websites asking for date of birth when age verification is not required
Forms requesting full addresses for simple inquiries
Mobile apps collecting contact lists unnecessarily
Job applications demanding personal details unrelated to the role
Excessive data collection increases breach impact and violates data minimization principles.
2. Using PII Beyond the Original Purpose
PII is often misused when it is repurposed without user awareness or consent.
Common scenarios:
Using customer data collected for support to run marketing campaigns
Sharing lead data internally for unrelated business activities
Reusing historical customer data after service termination
Expanding data use without updating privacy notices
Purpose creep is a frequent trigger for regulatory action.
3. Insecure Sharing of PII Internally
PII misuse frequently occurs inside organizations.
Examples:
Sharing spreadsheets with personal data via email
Storing PII on personal devices
Granting broad access to shared folders
Using unsecured messaging platforms for sensitive discussions
Internal misuse often goes undetected because it involves authorized users.
4. Exposing PII Through Misconfigured Systems
Misconfiguration is one of the largest sources of PII exposure.
Real-world issues include:
Publicly accessible cloud storage buckets
Unprotected backup files
Test environments using real customer data
Open databases indexed by search engines
These incidents are often discovered by third parties not by the organization itself.
5. Selling or Sharing PII Without Proper Disclosure
Some organizations misuse PII by monetizing it improperly.
Examples:
Selling customer data to third parties
Sharing marketing lists without consent
Allowing partners to reuse data beyond scope
Embedding trackers that share user data silently
Such practices frequently lead to fines, lawsuits and reputational damage.
6. Poor PII Handling by Third-Party Vendors
Even when organizations follow good practices, vendors may not.
Examples:
Marketing platforms mishandling contact lists
Support vendors accessing unnecessary personal data
Contractors downloading data to personal systems
Weak vendor security controls leading to exposure
Organizations remain accountable for vendor misuse.
7. Retaining PII Longer Than Necessary
Outdated data is a major risk factor.
Common issues:
Keeping inactive customer records indefinitely
Retaining former employee data beyond legal needs
Storing old backups without review
Archiving data without security controls
Many breaches involve data that should have been deleted years earlier.
8. Using Real PII in Testing and Development
Using production data in non-production environments is a frequent mistake.
Examples:
Developers copying live databases for testing
QA environments lacking security controls
Contractors accessing test systems with real PII
These environments are often less secure, making them prime targets.
9. Weak Access Controls and Oversharing
PII misuse often stems from excessive permissions.
Examples:
Employees accessing data outside their role
Former employees retaining system access
Shared accounts without accountability
Lack of access reviews
Oversharing turns internal users into accidental threats.
10. Ignoring User Requests Related to PII
Failing to act on data rights requests is also a form of misuse.
Examples:
Not deleting data upon request
Delayed responses to access requests
Incomplete data removal
Lack of visibility into stored PII
Regulators increasingly treat such failures as serious violations.
Is PII the Same Everywhere?

No PII is not defined or treated the same everywhere. While the core idea of protecting personal information is universal, what qualifies as PII and how it must be handled varies by country, region, industry and context.
This variation is one of the biggest challenges for organizations operating across borders.
Differences in Legal Definitions
Different laws use different terminology and scope.
Key variations include:
Some regulations define PII narrowly, focusing on direct identification
Others include technical and behavioral data
Some laws distinguish between sensitive and non-sensitive data
Others apply uniform protection to all personal data
As a result, the same dataset may be regulated differently depending on jurisdiction.
Treatment of Online Identifiers
One major point of difference is online and technical identifiers.
Examples:
IP addresses may be considered personal data in some regions
Device identifiers may trigger privacy obligations elsewhere
Cookies linked to individuals can be regulated in certain jurisdictions
Anonymous data may lose its status if re-identification is possible
This creates compliance complexity for websites, mobile apps and SaaS platforms.
Public vs Private Data Expectations
Some regions treat publicly available data differently.
Key distinctions:
Public data may still be protected if it identifies a person
Professional information may receive lighter treatment
Public records may still require safeguards
Context of use matters more than data source
Being publicly accessible does not automatically remove PII obligations.
Industry-Specific Variations
PII rules can change based on the sector.
Examples:
Healthcare data is subject to stricter controls
Financial data faces enhanced monitoring
Telecommunications data often has retention restrictions
Education data may have child-specific protections
Industry context can elevate ordinary PII into a higher-risk category.
The escalation of the israel iran war has raised global cybersecurity concerns, as attacks linked to geopolitical tensions often spread beyond the original conflict zone.
Cultural and Regulatory Expectations
Privacy expectations differ culturally as well as legally.
In some regions:
Consent is the default requirement
Individuals expect transparency and control
Data usage without disclosure is heavily scrutinized
In others:
Business usage may be more permissive
Regulatory enforcement may vary
Sector-specific oversight dominates
Understanding local expectations is as important as understanding the law.
Cross-Border Data Transfer Challenges
When PII moves across borders, additional requirements often apply.
Common issues include:
Data localization rules
Transfer impact assessments
Contractual safeguards
Regulatory approvals
What is acceptable within one country may be restricted when data crosses borders.
Check out our latest blog on Why Phishing Is Not Often Responsible for PII Data Breaches
Practical Impact on Organizations
These differences affect:
Data architecture decisions
Vendor selection
Cloud region choices
Privacy policy language
Consent mechanisms
Incident response planning
Organizations must design systems that can adapt to the strictest applicable standard.
Best Practice Approach
To manage global variation, many organizations:
Apply the highest common privacy standard
Classify data conservatively
Limit unnecessary data collection
Centralize governance while localizing execution
This reduces risk and simplifies compliance.
Check out our latest blog on Cybersecurity High-Speed Internet for the US Navy | Guide
Final Thoughts
Personally Identifiable Information is no longer just a compliance checkbox it is a core business risk and responsibility. From websites and SaaS platforms to internal systems and third-party vendors, PII flows through nearly every digital process.
What separates resilient organizations from vulnerable ones is not how much data they collect, but how intentionally they manage it.
Clear classification, minimal collection, strong controls and continuous oversight are what turn PII protection into a competitive advantage rather than a liability.
In a world of rising cyber threats and tightening regulations, treating PII with care is not optional it is essential for trust, growth and long-term sustainability.
Want to see how PII protection could work for your site or business?
Get in touch with me. I’d be happy to take a look and offer advice based on what’s worked for me.
Check out our recent blog on Cybersecurity Stocks: Growth, Risks & Returns
Frequently Asked Questions
Can business contact information still be considered PII?
Yes. Business contact details can still qualify as PII if they identify an individual, especially when linked to a specific role, organization, or digital account.
Is encrypted PII still considered personal data?
Yes. Encryption protects PII but does not change its classification. Encrypted data is still PII because it can be decrypted and linked back to an individual.
Does deleting a user account automatically remove all PII?
Not always. PII may still exist in backups, logs, analytics systems, or third-party tools unless deletion processes are designed to remove data across all systems.
Can internal employee data cause compliance issues?
Yes. Employee records, access logs and internal communications can all contain PII and are subject to the same privacy and security obligations as customer data.
Is anonymized data always safe from privacy laws?
Only if anonymization is irreversible. If data can be re-identified using reasonable methods, it may still fall under privacy regulations.