Table of Contents
Cyber threat hunting is the proactive practice of searching networks, endpoints, cloud systems, and user behavior to uncover hidden threats before automated tools detect them. It helps you reduce breach risk, shorten attacker dwell time, and improve overall security resilience.
Most organizations invest heavily in security tools. Firewalls filter traffic, antivirus blocks known malware, SIEM systems collect logs, and endpoint tools generate alerts. Those defenses matter, but modern attackers know how to avoid them.
They use stolen credentials, trusted admin tools, encrypted channels, and low-noise techniques that blend into normal activity. That means threats can remain active for weeks or months before someone notices.
This is where cyber threat hunting becomes essential.
Instead of waiting for alarms, you proactively search for suspicious behavior, hidden persistence, lateral movement, and early indicators of compromise across your environment. You assume something may have slipped past automated controls and actively investigate.
If you run a business, manage IT, or lead a SOC team, threat-hunting cybersecurity practices can dramatically improve detection speed and reduce damage from advanced attacks.
In this guide, you’ll learn what cyber threat hunting is, how the process works, the best threat hunting tools, how to choose a threat hunting platform, and when to consider managed threat hunting services.
You can also explore our best laptop for cyber security guide to find the right device for security testing, SOC work, virtualization, and everyday cybersecurity tasks.
What Is Cyber Threat Hunting?

Cyber threat hunting is the proactive process of searching your internal systems to identify malicious activity that security tools may have missed.
Traditional tools often depend on signatures, known patterns, or preset rules. Threat hunters go beyond those limits by looking for attacker behaviors.
They investigate signs such as:
Suspicious login activity
Credential misuse
Privilege escalation
Malware persistence
Unusual PowerShell usage
Rare outbound connections
Lateral movement between devices
Data exfiltration attempts
That’s why threat hunting has become one of the most valuable layers in modern defense programs.
If you’ve ever asked what threat hunting is, the simple answer is this:
It means actively searching for threats before they become incidents.
Check out our latest blog on Cybersecurity vs Data Analytics in 2026
Why Threat Hunting Matters in Cyber Security
Many businesses believe prevention tools are enough. Unfortunately, prevention alone rarely stops every attack.
Threat actors now rely on:
Phishing campaigns
Credential theft
Insider abuse
Cloud misconfigurations
Zero-day exploits
Living-off-the-land tactics
Remote access misuse
That is why threat hunting cybersecurity programs matter so much today.
Key Benefits
1. Faster Threat Detection
You discover suspicious behavior before automated systems escalate it.
2. Lower Breach Costs
Earlier containment usually means lower recovery costs.
3. Better Security Visibility
Threat hunts reveal blind spots in logs, telemetry, and tooling.
4. Stronger Incident Response
Hunters often identify attack paths before full compromise occurs.
5. Reduced Ransomware Risk
Many ransomware campaigns leave warning signs before encryption starts.
6. Continuous Security Improvement
Every hunt improves future detections and security processes.
How the Cyber Threat Hunting Process Works

The cyber threat hunting process follows a repeatable cycle.
1. Create a Hypothesis
Hunters begin with an assumption based on intelligence or suspicious trends.
Examples:
A privileged account may be compromised
PowerShell may be abused on endpoints
Attackers may be moving laterally
Cloud admin access may be misused
2. Gather Data
Hunters review:
Endpoint telemetry
SIEM logs
DNS records
Firewall events
Authentication logs
Cloud audit logs
Email security alerts
3. Investigate Patterns
Search for anomalies such as:
Impossible travel logins
New scheduled tasks
Rare process execution
Midnight file transfers
4. Validate Findings
Determine whether behavior is malicious or benign.
5. Improve Controls
Every completed hunt should strengthen detections and response workflows.
Best Threat Hunting Tools for Security Teams
Strong hunting requires visibility and fast investigation workflows. The best threat hunting tools help analysts search, correlate, and respond quickly.
Tool Category | Purpose | Example Use |
|---|---|---|
EDR/XDR | Endpoint activity visibility | Process and device hunts |
SIEM | Centralized log search | Multi-source correlation |
NDR | Network behavior analytics | Beaconing detection |
SOAR | Automated response | Faster containment |
IAM Analytics | Identity misuse detection | Suspicious logins |
Threat Intel | IOC enrichment | Actor tracking |
What to Look For
Choose tools that offer:
Fast search performance
Long-term log retention
MITRE ATT&CK mapping
Endpoint telemetry
Cloud integrations
Identity visibility
Automation support
How to Choose a Threat Hunting Platform
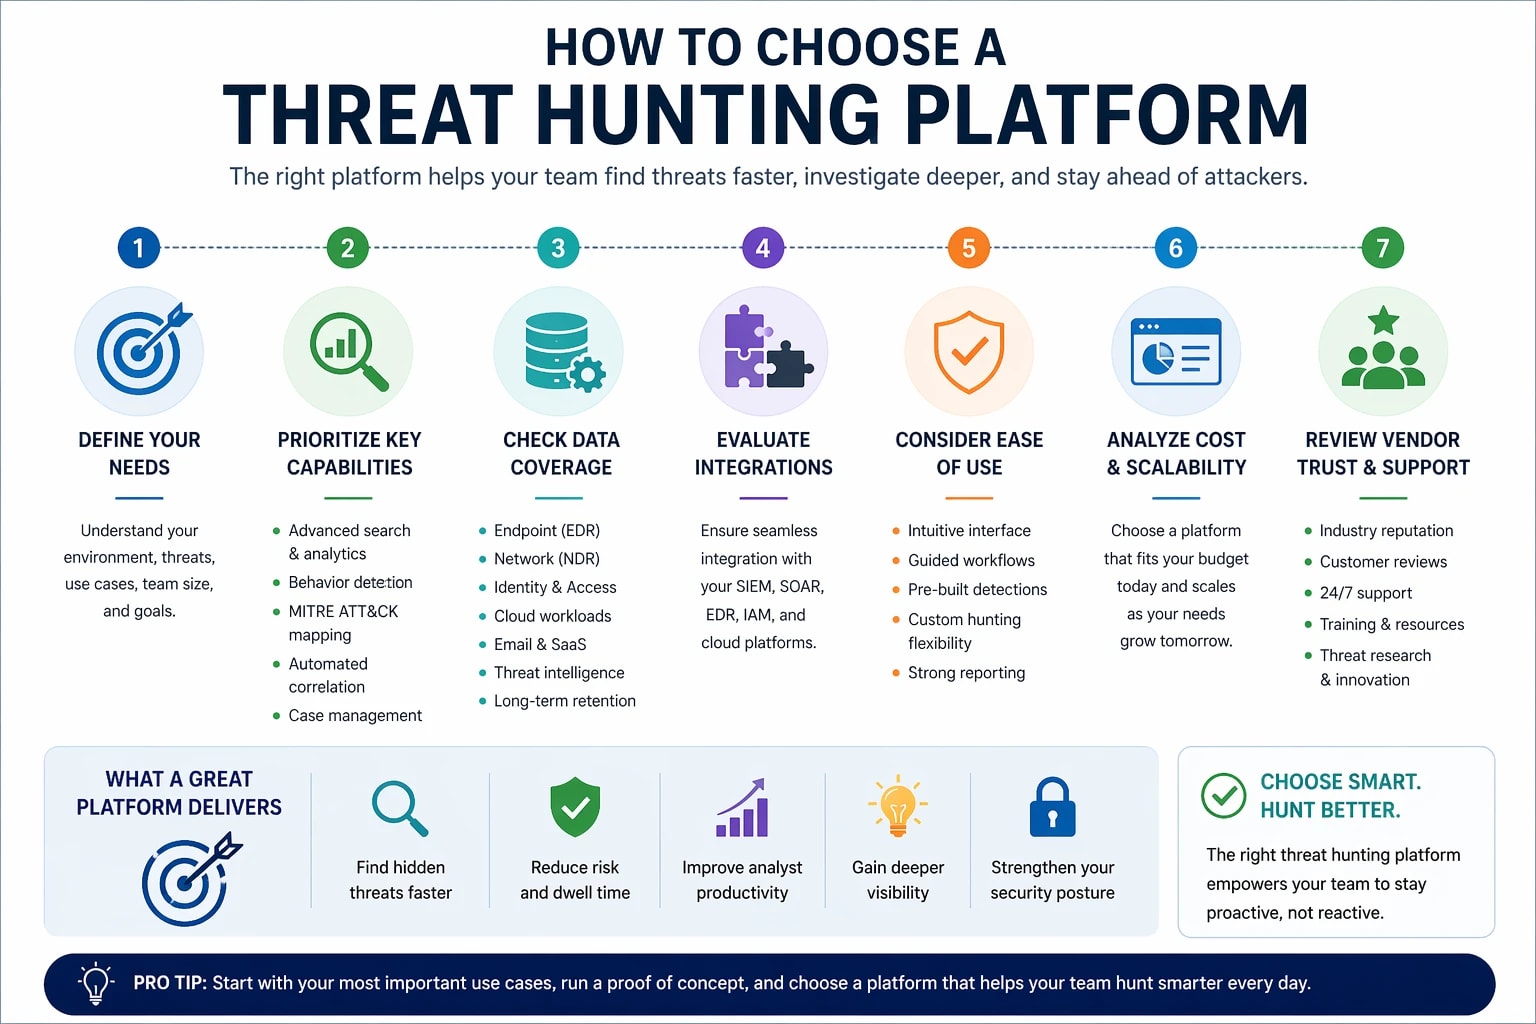
A modern threat hunting platform should do more than collect data.
You want a platform that helps analysts investigate efficiently.
Important Features
Unified dashboards
Query speed
Endpoint response actions
Alert enrichment
Threat intelligence integration
Cloud telemetry support
Automation playbooks
Many organizations compare multiple threat hunting platforms before deciding.
The best option depends on your environment size, compliance needs, and analyst maturity.
Threat Hunting Indicators of Compromise
One high-value hunting activity is identifying threat hunting indicators, more naturally known as indicators of compromise.
These indicators may include:
Malware hashes
Suspicious domains
Unusual IP addresses
Persistence registry keys
Credential dumping behavior
Suspicious scripts
Unauthorized admin accounts
Hunters use these indicators as starting points, but strong teams also look beyond known IOCs into behavioral signals.
Threat Hunting Techniques Used by Experts

Successful programs use several threat hunting techniques.
Intelligence-Based Hunting
Use threat feeds, malware reports, and actor TTPs.
Hypothesis-Based Hunting
Start with assumptions like:
Attackers may use a remote desktop after phishing.
Anomaly-Based Hunting
Find behavior outside normal baselines.
Examples:
User logs in at odd hours
The device sends unusual traffic
Rare tools launch across hosts
MITRE ATT&CK Hunting
Map hunts to attacker tactics such as:
Persistence
Discovery
Lateral movement
Credential access
Exfiltration
Real Cyber Threat Hunting Examples
Examples make the value of cyber threat hunting clear.
Example 1: Stolen Credentials
A user logs in from New York and then 15 minutes later from Europe.
Threat hunters identify impossible travel, force password resets, and block access.
Example 2: Ransomware Precursors
Multiple endpoints suddenly run discovery commands.
Hunters isolate devices before encryption begins.
Example 3: Insider Data Theft
An employee downloads thousands of files before resignation.
Hunters escalate and preserve evidence.
Example 4: Cloud Misuse
A new privileged role appears in AWS after business hours.
Hunters investigate unauthorized privilege escalation.
Threat Hunting vs Threat Intelligence
These terms are often confused.
Category | Threat Hunting | Threat Intelligence |
|---|---|---|
Goal | Find active threats internally | Understand external threats |
Focus | Your environment | Threat actors and campaigns |
Data | Logs and telemetry | Reports and feeds |
Outcome | Detection | Better decisions |
Threat intelligence tells you what may happen.
Threat hunting tells you whether it is already happening.
Threat Hunting Solutions for Growing Businesses
Many companies need scalable threat hunting solutions but lack large internal teams.
Common options include:
In-house SOC hunting teams
MDR providers
Co-managed SOC services
Managed EDR + hunting bundles
Consulting-led maturity programs
The best solution depends on budget, staffing, and risk profile.
Managed Threat Hunting Services Explained
Managed threat hunting gives you access to experienced analysts without building a full internal team.
These threat hunting services often include:
Continuous monitoring
Expert investigations
Incident escalation
Threat intelligence support
Monthly reporting
Detection tuning
Best For
SMBs with lean IT teams
Mid-sized companies needing 24/7 help
Enterprises needing after-hours coverage
Pros
Faster maturity
Access to experts
Lower hiring pressure
Better coverage
Cons
Monthly recurring cost
Vendor dependence
Requires trust and onboarding
Proactive Threat Hunting Best Practices

Strong proactive threat hunting programs follow consistent habits.
Hunt High-Value Assets First
Prioritize:
Domain controllers
Executive accounts
Finance systems
Production workloads
Cloud admin roles
Hunt Regularly
Weekly or monthly hunts outperform occasional reviews.
Track Metrics
Measure:
Mean time to detect
Threats uncovered
Detection gaps closed
Response speed
Improve Logging
You cannot hunt what you cannot see.
Common Threat Hunting Scenarios
Insider Threat Hunting
Look for:
Mass downloads
Access misuse
Privilege abuse
Data transfers before resignation
Ransomware Precursors
Watch for:
Backup deletion attempts
Credential dumping
Network discovery
Lateral movement
Cloud Threat Hunting
Investigate:
New API keys
Suspicious console logins
Unusual storage access
Unauthorized admin roles
Identity Threat Hunting
Monitor:
MFA fatigue attacks
Impossible travel
Token abuse
Password spray attempts
Future Trends in Threat Hunting

The future of threat hunting cyber security will include:
AI-Assisted Investigations
AI helps summarize alerts, prioritize risk, and surface anomalies.
Identity-Centered Hunting
As credentials become prime targets, identity telemetry matters more.
Cloud-Native Hunting
More organizations now need AWS, Azure, and SaaS visibility.
Automated Response
Platforms increasingly isolate hosts or disable accounts automatically.
Continuous Hunting Models
Instead of scheduled hunts, mature teams hunt constantly.
Final Thoughts
Cyber threat hunting has become one of the smartest ways to strengthen modern defense.
Attackers no longer depend only on noisy malware. They use legitimate tools, valid credentials, and stealth tactics designed to avoid detection.
If you wait for alerts, you may already be behind.
When you invest in threat hunting, you move from reactive defense to active security operations. You detect hidden threats faster, reduce breach impact, and continuously improve resilience.
Whether you build internally, buy threat hunting solutions, or outsource through managed threat hunting, the key is starting now.
Frequently Asked Questions
What is cyber threat hunting?
Cyber threat hunting is the proactive search for hidden threats or suspicious activity inside your systems before automated tools detect them.
What are the best threat hunting tools?
The best threat hunting tools usually include EDR, SIEM, NDR, IAM analytics, and threat intelligence platforms.
What is a threat hunting platform?
A threat hunting platform is software that helps analysts investigate logs, endpoint behavior, identities, and network events in one place.
Are managed threat hunting services worth it?
Yes. Managed threat hunting can be cost-effective for businesses lacking internal security staff or 24/7 coverage.
Why is proactive threat hunting important?
Proactive threat hunting helps find threats early, reduce attacker dwell time, and prevent costly incidents.